Invoice Fraud Prevention: Checks Before Changing Supplier Bank Details
/ Key takeaways
- Verify the change before releasing the payment
- A supplier-bank-change workflow for a small team
- Make the check usable when someone is under pressure
Verify the change before releasing the payment
Invoice fraud prevention starts by treating a change to supplier bank details as a separate, independently verified request. Use a trusted contact route already held in your supplier record, record the check and require the appropriate approval before updating the payment details. A convincing email thread is not enough.
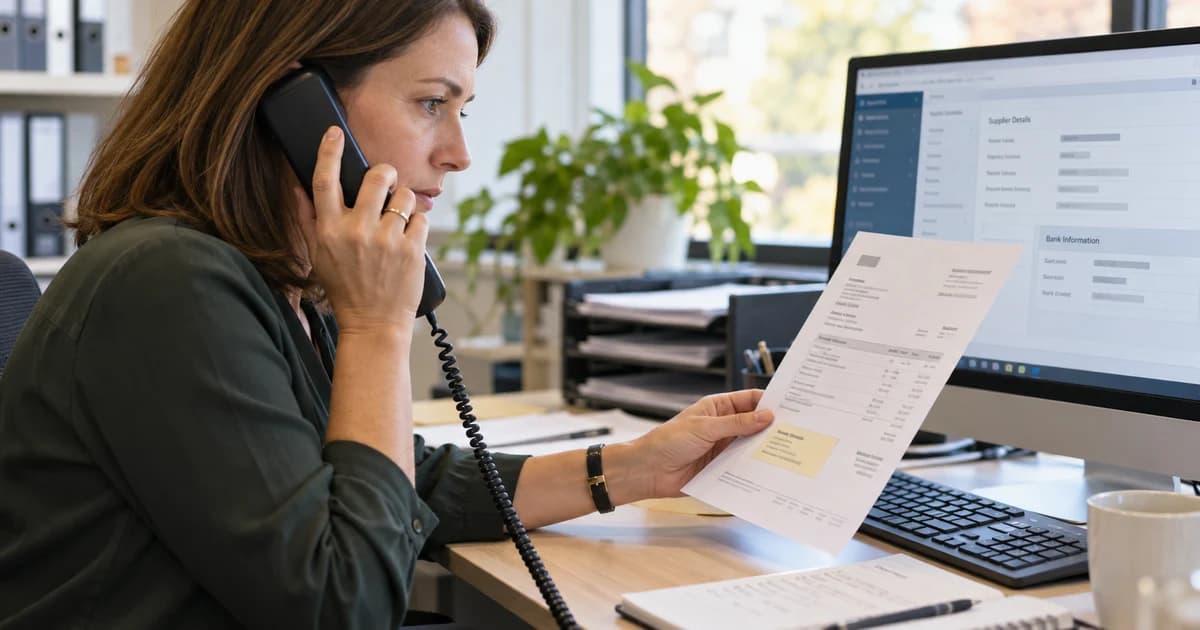
The awkward request usually looks ordinary: a familiar invoice, an approaching due date and a short note saying the supplier's account has changed. The person processing it may be trying to keep a project moving. A useful process gives that person a clear reason to pause, without needing them to prove that the email is fraudulent.
A supplier-bank-change workflow for a small team
| Step | Check | Owner |
|---|---|---|
| Hold the change | Separate the invoice from the request to amend bank details. Mark the payment as awaiting verification. | Accounts payable |
| Use a trusted route | Contact an authorised supplier representative using a previously verified record, not the new email's number. | Assigned verifier |
| Record the result | Keep the date, contact, method and outcome in the approved supplier-change record. | Assigned verifier |
| Approve the amendment | Apply the business's required approval and separation of duties before changing the supplier record. | Authorised approver |
| Release and review | Check the approved payment destination and reconcile the result through your normal process. | Payment owner |
The table is a suggested operating record, not a banking rule. Your finance lead should set the approval limits, approved verification channels and exceptions. A sole operator may need a different arrangement from a team with separate supplier-management and payment roles.
Make the check usable when someone is under pressure
Consider a fictional property-management business paying a contractor before a handover. The invoice matches the job, but a reply asks for payment into a different account that afternoon. The office manager calls the contact already held in the supplier record. The supplier says no change was requested. The payment stays on hold while the team investigates. This is an illustrative scenario, not a BPro client story.
Notice what the example does not depend on: spotting a spelling mistake or persuading the caller that the sender looked suspicious. The rule applies to every bank-detail change. Write down what staff should do if the contact cannot be reached, the approver is absent or someone asks to bypass the process.
A second person should have enough evidence to challenge the change, rather than just repeating an approval click. Where possible, separate the ability to amend a supplier record from the ability to release a payment. Decide how the checks work for new suppliers as well as changes to existing ones.
Email security supports the process
A fraudulent message can use a lookalike domain, a spoofed sender or a genuinely compromised mailbox. That is why a familiar display name, valid signature block or existing conversation does not prove that the payment instruction is authorised.
Protect the accounts handling invoices: use appropriate multi-factor authentication, review unusual sign-ins and mailbox rules, restrict unnecessary access and provide a simple way to report suspicious messages. Email authentication and filtering help reduce exposure, but they do not approve payments for your business. A validly authenticated message from a compromised account can still carry fraudulent instructions.
Keep supplier contact records under access controls too. If an attacker can replace the trusted phone number as easily as the bank account, the callback process has lost its independent reference. Review who can amend those records and what evidence is retained.
If money has already been sent, act promptly
Contact your bank immediately through its trusted fraud channel and explain the suspected payment diversion. Ask what recovery steps are available; recovery is not guaranteed. Follow the relevant reporting process for your jurisdiction. The FBI's guidance for US incidents includes reporting to IC3, while the NCSC provides a response route for UK organisations.
Preserve the original messages, payment records and relevant account logs. Involve your IT or security team to assess mailbox access, sessions, forwarding rules and other affected accounts. Notify the appropriate people under your organisation's response process, including your insurer or advisers where relevant. Do not let a follow-up message from the suspected attacker steer the investigation.
- Bank-detail changes are independently verified before payment.
- The trusted supplier contact record has a documented owner.
- Approval evidence is retained in an appropriate restricted system.
- Staff know how to hold an urgent payment and report a concern.
- Finance mailboxes have reviewed access, sign-in protection and escalation contacts.
BPro's cybersecurity support can help review the mail and identity controls around this process. The Microsoft 365 security checklist covers the account baseline, and our passkey rollout guide explains sign-in planning. Payment authority and supplier verification remain business decisions.
Review the email controls around your payment process
Tell us which mail platform you use and how suspicious payment requests are escalated. We can review the technical exposure and document a practical next step.
Get Free IT Assessment/ Article map
Verify the change before releasing the payment
A supplier-bank-change workflow for a small team
Make the check usable when someone is under pressure
Email security supports the process
If money has already been sent, act promptly
Sources
Frequently Asked Questions
What is invoice redirection fraud?
It is an attempt to redirect a legitimate payment to an unauthorised account, often through a forged or compromised email conversation asking for changed bank details. The invoice itself may appear genuine.
How should we verify changed supplier bank details?
Use a trusted, previously verified contact route and an authorised supplier representative. Keep a record of the check and apply your approved supplier-change and payment controls. Do not rely on contact details supplied in the change request.
Does multi-factor authentication prevent invoice fraud?
It helps protect accounts, but it does not verify a payment instruction or stop every scam. Combine account security with independent supplier verification, approval controls and a clear reporting process.
What should we do if we paid a fraudulent invoice?
Contact your bank immediately using its trusted fraud channel, preserve payment and message records, involve your security team and follow the relevant local reporting process. The bank can advise on possible recovery, which is not guaranteed.
/ Choose the next step
Move from article guidance to a practical review path.
Pick the route that best matches the issue behind the article so the next conversation starts with the right scope.
Assessment path
Review your email and account controls
Share your mail platform, main concern and existing controls. The assessment identifies a practical next step.
Service path
See cybersecurity coverage
Review identity protection, email security, endpoint coverage and incident escalation under an agreed scope.