01
Signal
Controlled Cost Optimization
We right-size resources, apply Reserved Instance or Savings Plan pricing, eliminate waste, and set up cost monitoring with alerting, so cloud spend matches actual business needs.
Cloud support for growing businesses across Azure, AWS, Google Cloud, Microsoft 365, Google Workspace, SharePoint, Intune, VPS, backup, identity, and hosted workloads. We map dependencies, access, recovery, cost, and handover before a migration or operating change.
Scope, ownership, reporting, and handover confirmed before delivery starts.
/ Direct answer
Cloud support services from BPro Technologies help businesses plan, migrate, secure, govern, and operate cloud and productivity environments. Work can include Microsoft 365, Azure, Google Workspace, identity settings, backup readiness, cost review, access control, resilience planning, and operating documentation so cloud decisions, dependencies, and handover paths stay visible.
/ Cloud operating model
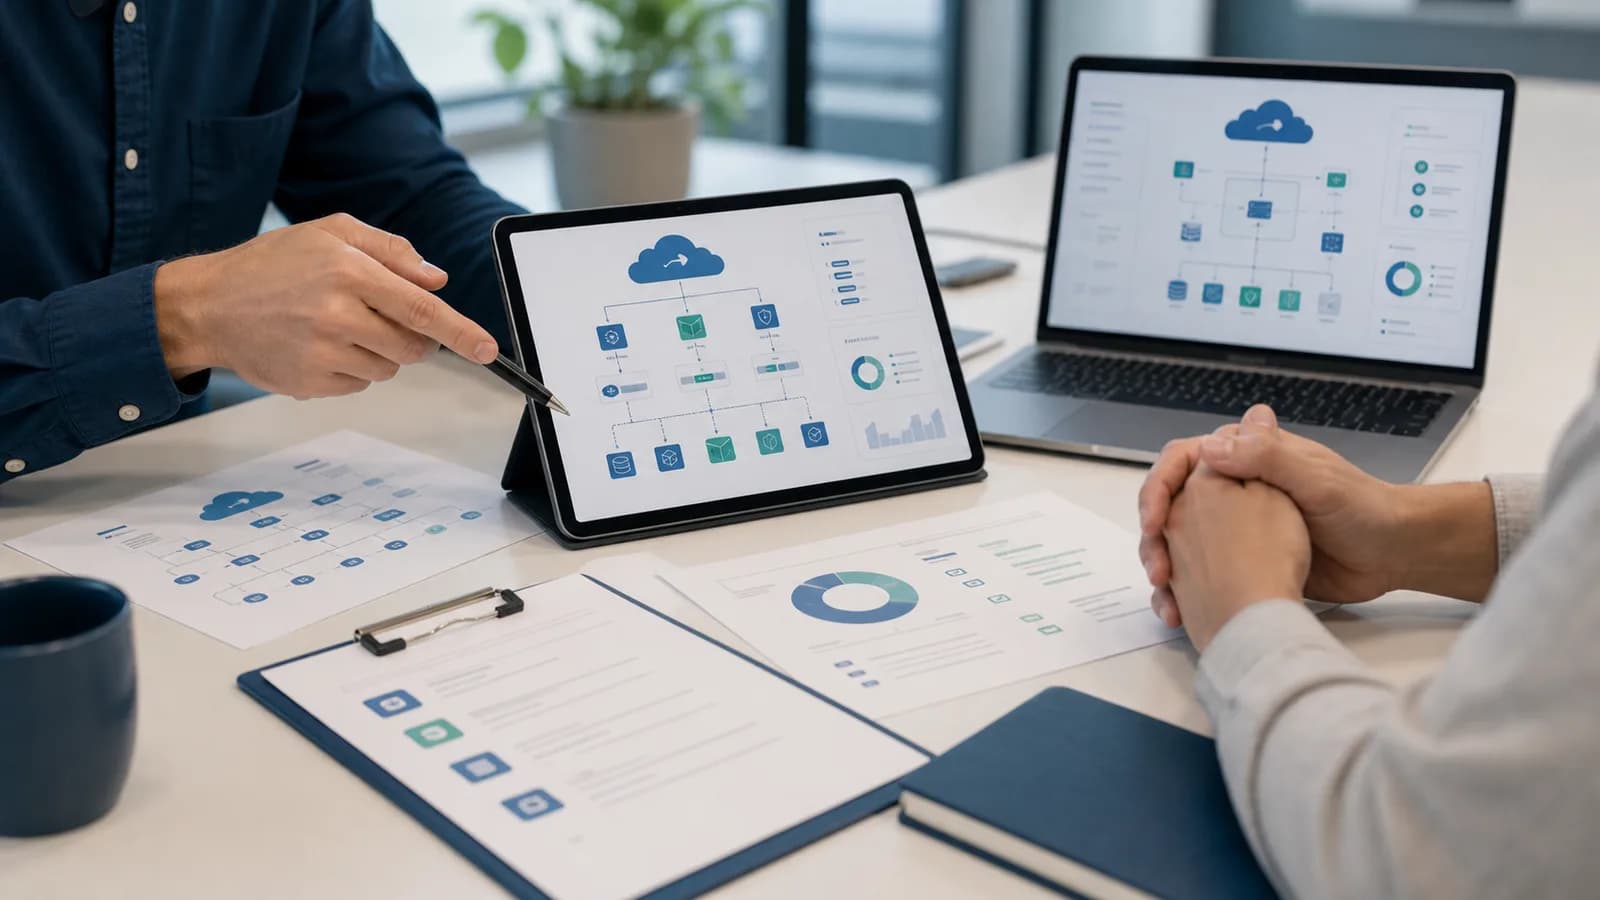
Cloud maturity depends on more than migration speed. This model connects current-state assessment, architecture, governance, resilience, cost visibility, and ongoing operations.
Migration path
Applications, data, dependencies, identity, and cost baseline.
Workload fit, risk, compliance, licensing, and migration path.
Waves, rollback criteria, test plan, cutover ownership.
Landing zone, network, compute, storage, backup, and identity.
Access, tagging, policy, monitoring, and security controls.
Cost review, resilience checks, patching, and reporting cadence.
Architecture layers
Applications, databases, file stores, SaaS tenants
Compute, storage, network, CDN, managed services
Identity, policy, tags, logging, backup, access
Monitoring, cost review, patching, incident path
/ Operational view
Start with the systems and risks in scope, agree access and change controls, then track remediation and review the results.
01
Signal
We right-size resources, apply Reserved Instance or Savings Plan pricing, eliminate waste, and set up cost monitoring with alerting, so cloud spend matches actual business needs.
02
Control
Cloud resources scale up during peak demand and down when not needed, without hardware procurement lead times or capital expenditure commitments.
03
Response
We design the target cloud architecture, define migration waves (starting with lowest-risk workloads), establish security baseline, and produce a detailed migration runbook with rollback procedures.
04
Evidence
After go-live, we monitor performance, optimize costs, apply security hardening, and confirm backup and DR configurations. A 30-day post-migration review closes any open items.
/ Proof to review
Buyer-friendly samples and checklists make the delivery model easier to inspect before a call.
Systems, vendors, incidents, access, and reporting mapped to clear owners.
Open risks, mitigation status, severity, and next action tracked in one view.
Runbooks, diagrams, access notes, configuration records, and escalation paths.
/ Ownership model
A quieter, inspectable model for what gets reviewed, managed, reported, and handed over.
Configured around the systems, identities, and risks that matter most.
Escalation routes and response windows confirmed after discovery.
Policy baselines, evidence records, and recurring review cadence.
Prioritized fixes with ownership, status, and next action tracking.
/ Risk matrix
These are the operational signals that usually mean the risk is no longer theoretical.
Aging hardware means rising maintenance costs, performance bottlenecks, and increasing risk of failure. Every year you delay, technical debt compounds and the migration cost grows.
Migrating to the cloud without proper architecture and governance often results in costs that exceed on-premise spend. Over-provisioned instances, idle resources, and unmanaged storage are silent budget drains.
Provisioning physical hardware takes weeks. Cloud resources can be deployed in minutes, but only with the right architecture, automation, and access controls in place first.
The cloud shared responsibility model means you still own your data security, identity configuration, and access controls. Many businesses migrate without addressing these and create serious exposure.
/ Buyer outcomes
A serious cloud solutions partner should make scope, ownership, evidence, and handoff visible.
We right-size resources, apply Reserved Instance or Savings Plan pricing, eliminate waste, and set up cost monitoring with alerting, so cloud spend matches actual business needs.
Cloud resources scale up during peak demand and down when not needed, without hardware procurement lead times or capital expenditure commitments.
We apply IAM hardening, network segmentation, encryption, CSPM, and compliance alignment from the start. Security is built into the architecture, not added as an afterthought.
Multi-AZ deployments, automated failover, and cloud-native backup services ensure your workloads survive individual component failures without manual intervention.
/ Scope map
The practical work BPro Technologies can own, document, and report for cloud solutions.
We evaluate your current applications, data, and infrastructure to determine cloud suitability, classify workloads using the 6 Rs framework, model true migration costs, and recommend the right platform for each service.
Structured migration execution: cutover planning, data transfer, DNS changes, parallel-run testing, go-live validation, and rollback notes. We plan for controlled transitions and reduced disruption instead of assuming every migration can be invisible to users.
Architecture designed against AWS Well-Architected, Microsoft Azure Well-Architected, or Google Cloud Architecture Framework principles, covering reliability, security, performance, cost optimization, and operational excellence.
Ongoing management of your cloud and hosted estate: resource monitoring, cost review, patch management, access control reviews, backup oversight, and incident response.
Analysis of your current cloud spend, identification of waste (idle resources, oversized instances, forgotten storage), Reserved Instance strategy, and ongoing cost governance with monthly reporting.
Terraform, Azure Bicep, or CloudFormation for repeatable, version-controlled infrastructure. CI/CD pipeline setup with GitHub Actions, Azure DevOps, or AWS CodePipeline to automate testing and deployment.
Cloud Security Posture Management to detect misconfigurations, IAM review and hardening, encryption policy enforcement, security group audits, and compliance alignment with CIS Benchmarks and cloud-native security tools.
Tenant setup or migration, license optimization, Conditional Access or context-aware access, Microsoft Entra ID, Google Workspace administration, Intune device enrollment, SharePoint, Teams, Drive, and collaboration governance.
Management of practical hosted environments beyond hyperscale cloud: VPS platforms, DNS, CDN, object storage, application hosting, backup targets, monitoring, and handover documentation.
/ Engagement terms
Clear boundaries help buyers compare cloud solutions without assuming every task, license, project, or access path is included by default.
Environment review, priority risks, monitoring approach, control gaps, and documented remediation path.
Response windows, access model, escalation owners, evidence cadence, and change approval rules.
Major licensing changes, hardware purchases, compliance audits, legal review, and emergency remediation outside the agreed scope.
Remote work uses named accounts, least-privilege access, MFA, approval paths, and documented escalation instead of shared or informal access.
Monitoring, logs, configuration records, asset notes, and reporting give the service enough visibility to support decisions and response.
Tell us the service area, current tools, users, business impact, and preferred contact window.
We identify the right next step: assessment, project review, co-managed support, or ongoing managed service.
Any system access, change window, or implementation work starts only after approval and documented scope.
/ Scope and pricing factors
Pricing is confirmed after scope, systems, access, coverage, and delivery expectations are understood. These factors help buyers compare options without relying on assumptions.
Decision preview
Users, devices, cloud tenants, servers, networks, firewalls, backups, and admin roles affect the review and support scope.
Identity exposure, endpoint gaps, backup readiness, monitoring needs, and incident response expectations affect priority and effort.
Response targets, escalation paths, reporting cadence, and security evidence are confirmed by scope and agreement.
A free assessment helps confirm whether the next step is remediation, monitoring, cloud governance, or ongoing support.
/ Delivery timeline
A delivery path with defined evidence, decisions, and handoff points at every stage.
We inventory your current environment, classify workloads using the 6 Rs (Rehost, Replatform, Refactor, Repurchase, Retain, Retire), and produce a cost model comparing on-premise vs cloud for each workload.
We design the target cloud architecture, define migration waves (starting with lowest-risk workloads), establish security baseline, and produce a detailed migration runbook with rollback procedures.
We execute migration in controlled phases with parallel-run testing, data integrity validation, and user acceptance testing before each cutover. Rollback plans are in place for every wave.
After go-live, we monitor performance, optimize costs, apply security hardening, and confirm backup and DR configurations. A 30-day post-migration review closes any open items.
/ Buyer scenarios
Best-fit teams, environments, and business contexts for this service.
Scenario 01
Cloud-native infrastructure with auto-scaling, CI/CD pipelines, container orchestration (Kubernetes/ECS), and multi-region deployment for software products that need high availability and rapid release cycles.
Scenario 02
Elastic cloud infrastructure that scales automatically for seasonal peaks, paired with global CDN delivery, managed database services, and cost optimization during off-peak periods.
Scenario 03
HIPAA-compliant cloud environments for electronic health record systems, telemedicine platforms, and clinical data, with encryption, audit logging, access control, and Business Associate Agreement (BAA) coverage.
Scenario 04
High-availability cloud infrastructure with SOC 2 and PCI-DSS alignment, low-latency transaction processing, data residency controls, and financial-grade encryption and key management.
/ Specialist services
Detailed pages for the work buyers most often ask about by name.
A tenant-to-tenant move covers identity and user mapping, mailbox and OneDrive migration, SharePoint content, Teams structure, licensing, and domain cutover. The parts most often underestimated are permissions translation and anything hard-coded to the old tenant, such as shared mailboxes, app registrations, and integrations. It is normally staged in waves with a defined cutover window.
The 6 Rs categorize migration strategies per workload: Rehost (lift-and-shift, move as-is with no changes), Replatform (make targeted optimizations during migration, e.g., moving to a managed database service), Refactor (re-architect for cloud-native services to unlock scalability), Repurchase (replace with a SaaS product, e.g., switching from on-premise CRM to Salesforce), Retain (keep on-premise for now due to compliance or complexity), and Retire (decommission unused or redundant systems). We apply this framework during discovery to recommend the right approach for each workload rather than treating everything the same.
The right choice depends on your existing tools, licensing, workload type, and compliance requirements. Azure is typically the best fit for Windows-heavy environments with existing Microsoft 365 licensing. The integration between Microsoft Entra ID, Intune, and Azure services is a genuine advantage. AWS has a broad service catalog and strong third-party ecosystem. Google Cloud excels in data analytics, machine learning, and Kubernetes-native workloads. We help you evaluate objectively based on your actual requirements rather than vendor preference.
Yes. BPro Technologies can help plan Google Workspace to Microsoft 365 migrations including user mapping, mailbox migration, DNS cutover, Exchange Online setup, SharePoint file structure, permissions, Intune readiness, and post-migration checks.
Yes. SharePoint file sharing, document libraries, permissions, OneDrive, Intune enrollment, compliance policies, security baselines, and handover documentation can be included when the scope calls for Microsoft 365 workplace management.
Cost control starts in the architecture phase: right-sizing resources, choosing appropriate service tiers, and avoiding over-provisioned defaults. Post-migration, we apply Reserved Instance or Savings Plan pricing for predictable workloads, set up Cost Anomaly Detection alerts, implement tagging policies for cost allocation, and review spend monthly. FinOps is an ongoing practice, not a one-time exercise.
Infrastructure as Code (IaC) means defining your cloud infrastructure in configuration files using tools like Terraform, Azure Bicep, or AWS CloudFormation, that can be version-controlled, peer-reviewed, and applied consistently across environments. IaC eliminates manual configuration drift, enables full disaster recovery by rebuilding from code, makes your infrastructure auditable, and dramatically reduces the time to deploy new environments. We recommend IaC for any production cloud environment.
Yes. If you're already in AWS, Azure, or Google Cloud and need better management, security hardening, cost visibility, or operational support, we conduct a current-state assessment and transition management without requiring any migration or re-architecture. Many clients engage us specifically to clean up and optimize cloud environments that have grown organically without governance.
We use encrypted transfer protocols for all data in transit, minimize the window during which data exists in two places simultaneously, restrict access to migration accounts to essential personnel only, verify data integrity with checksums after each migration phase, and maintain a complete transfer log for compliance. For regulated data (health records, payment data), we align the migration process with applicable framework requirements.
A typical small to mid-sized cloud migration takes 4 to 12 weeks end to end. The first one to four weeks cover discovery and architecture, then workloads move in scheduled waves, often over weekends, to avoid weekday disruption. Simple Microsoft 365 or single-app moves can finish in days, while multi-server or compliance-heavy environments run longer and are phased deliberately.
A cloud migration RFP should make every provider state the same five things: how long discovery takes, what assumptions the estimate rests on, the delivery windows for each wave, the escalation path when a wave slips, and what is explicitly excluded. Compare those answers rather than headline durations. A provider who commits to a date before discovery is guessing, and that guess becomes your risk.
Cloud migration cost depends on how many workloads move, how much re-architecture they need, and your ongoing cloud consumption. The main drivers are the migration project itself (a fixed-scope fee after discovery) and your monthly cloud bill afterward. We size both in the assessment, apply Reserved Instance or Savings Plan pricing for predictable workloads, and give you a written estimate before any work starts.
Downtime depends on the workload and migration method. We migrate in phases with documented rollback criteria and a go or no-go checkpoint before each wave. Where a brief outage is unavoidable for a specific system, it is planned, communicated, and kept to a defined window.
FinOps is the practice of building cost visibility and accountability directly into how cloud is architected and operated, not reviewing the bill after the fact. We set up tagging, budgets, and cost alerts as part of the migration and management scope, so cost governance is running from day one rather than delivered as a one-time report.
It depends on your risk tolerance, existing tooling, and team skills. A single provider is simpler to manage and often cheaper at smaller scale. Multi-cloud adds resilience and negotiating leverage but adds operational complexity. We size this against your actual workloads during the assessment rather than defaulting to either answer.
We can architect for it if you expect AI workloads down the line, considering compute scaling, data access patterns, and cost controls upfront. If AI isn't on your near-term roadmap, we won't over-build for it, but we'll flag where a decision now would make it easier to add later.
Lift-and-shift moves workloads to the cloud largely as-is, which is faster and lower-risk but doesn't capture cloud-native cost or scaling benefits. A cloud-native rebuild re-architects the workload to use cloud services directly, which takes longer but performs and scales better long-term. We recommend which fits based on the workload, timeline, and budget, not a default preference.
Every cloud migration starts with a cloud strategy: what moves, what stays, what gets retired, and what it will cost to run afterwards. For Azure we use Azure Migrate to discover servers and size them, then move workloads in waves with testing and a rollback plan. AWS and Google Cloud moves follow the same pattern, and every migration ends with documentation, monitoring and a handover to ongoing operations.
Yes. BPro Technologies delivers remote services for businesses in the United States and United Kingdom. Every managed client receives 24/7 monitoring and helpdesk. Before work begins, we agree the systems in scope, response targets, and escalation contacts. Project and co-managed engagements have their own agreed scope. Physical work is handled by your team or chosen local provider.
Yes. Most work is delivered through secure remote access, approved admin accounts, ticketing, monitoring, documentation, scheduled calls, and defined escalation paths. If a task needs hands-on work, BPro Technologies documents the requirement so the client can use their own team or chosen local provider.
No. The first conversation can start with business context, current tools, users, risks, and goals. If deeper technical review is needed later, access is requested only after approval and is limited to the agreed scope.
BPro Technologies reviews the request, confirms the service area, asks for any missing context, and recommends the next step. That may be a free assessment, a fixed-scope project review, a support plan, or a more detailed discovery call.
Remote delivery relies on MFA, named accounts, least-privilege access, audit trails, documented change paths, and clear approval rules. The goal is to make access and decisions visible rather than informal.
/ Next step
We assess the current environment, model the cost of change, and recommend a practical platform, migration, or support path before you commit.
No commitment required - We usually respond within one business day