Process review
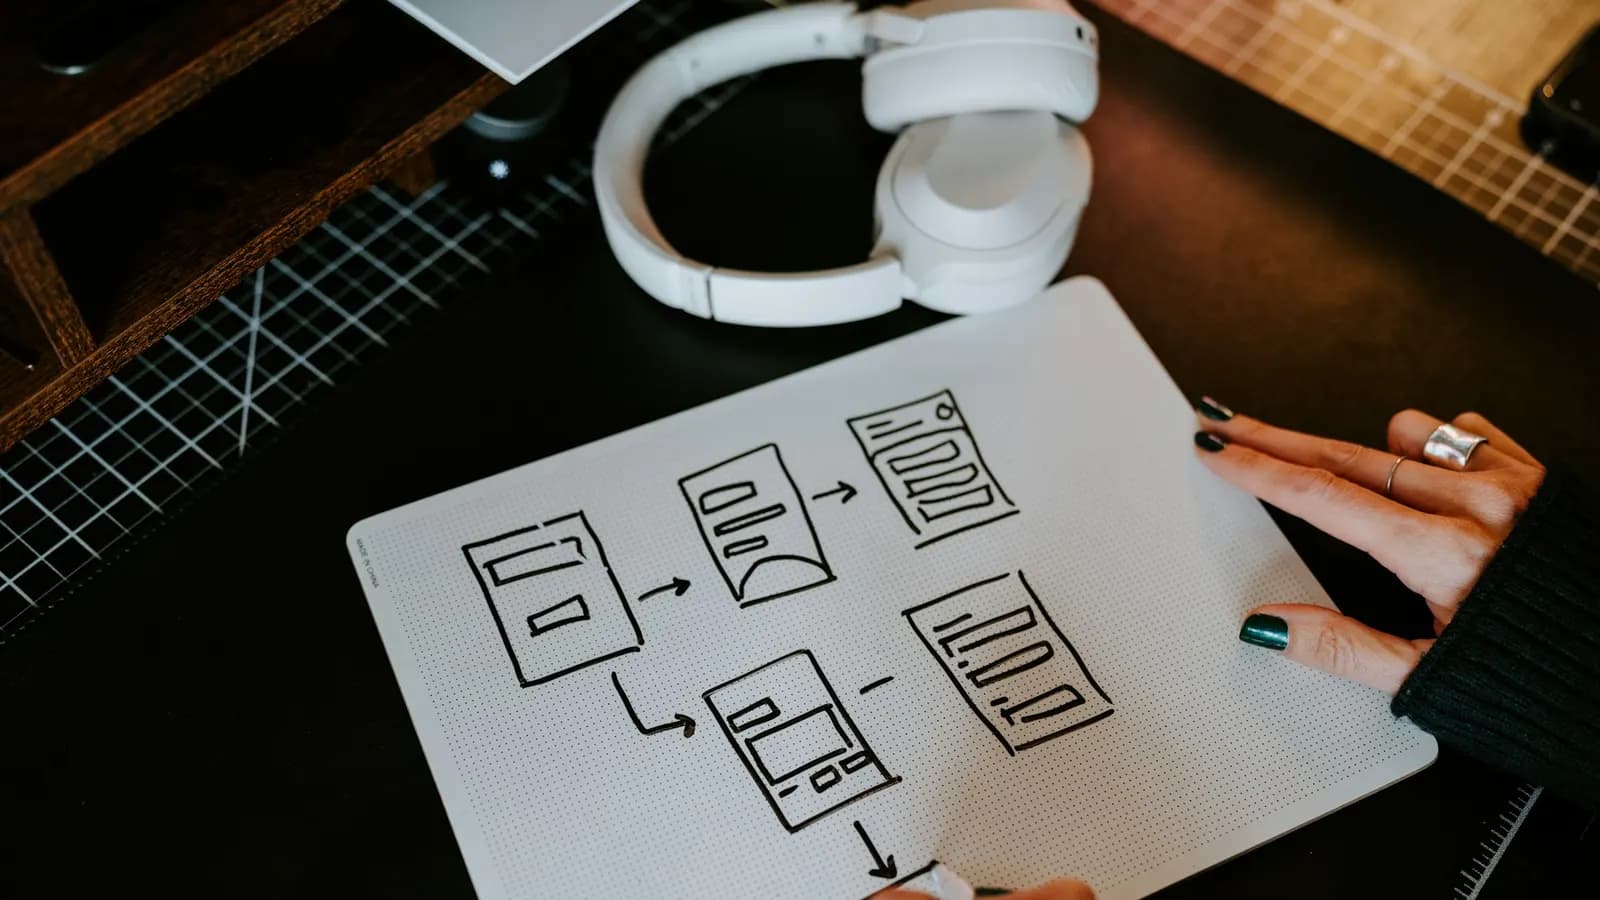
Map the trigger, inputs, approvals and exceptions.
A build/configure decision and the smallest useful workflow.
A new starter needs an account, a licence, the right groups, a laptop, a mailbox, access to three systems and a welcome email. Someone usually does all of it by hand, from a checklist that's slightly out of date. Automating that isn't glamorous, but it's where the hours go and where the mistakes happen.
/ Fit check
Best for
HR and IT teams with regular joiners and leavers on Microsoft 365 or Google Workspace
Not for
Processes that change every week and have no agreed owner
Deliverables
Process map, automated workflows, approval steps, audit logging and runbooks
/ Direct answer
Internal IT workflow automation consulting maps tasks such as onboarding, offboarding, role changes and access requests. Suitable steps can then be automated with approvals, failure handling and completion checks. Logs help the team investigate what happened; they need retention settings and monitoring rather than being treated as proof that every action succeeded.
/ Scope your engagement
BPro supports Power Automate and n8n workflows. Platform selection depends on existing licences, connectors, data handling and who will maintain the flow.
Map the trigger, inputs, approvals and exceptions.
A build/configure decision and the smallest useful workflow.
Connect approved actions using Power Automate or n8n.
Test cases, failure handling and an audit trail.
Agree connector ownership, credentials and change requests.
Monitoring and support responsibilities after release.
This example illustrates the record format. It is not a client result or a service-level commitment. Your proposal lists the deliverables and responsible people.
| Step | Workflow action | Control / exception |
|---|---|---|
| Request | Capture authorised joiner details and required systems | Validate the requester and avoid collecting unnecessary personal data |
| Approve and provision | Named owner approves access before permitted actions run | Record approval; pause if a connector or action fails |
| Verify and close | Check results, notify the owner and record the audit trail | Route partial completion for review instead of reporting success |
Current process, volume, tools, connector availability, approval owner and common failure cases.
/ 01
It starts in the HR system, or a structured form if there isn't one. A new starter record triggers account creation, licence assignment, group membership by role, mailbox and Teams setup, device assignment and a welcome pack, with manager approval for anything beyond the role's standard access. A role change adjusts groups. A leaver record triggers offboarding on the right date.
New record, role change or leaving date in HR, or a submitted form.
Groups and licences come from the role, not from copying another user.
Anything beyond the standard goes to the manager or system owner.
A laptop is assigned and the new starter gets sign-in instructions for day one.
Record outcomes, flag failures and reconcile completed actions against the requested changes.
/ 02
At the authorised leaving time, block sign-in and revoke sessions, then verify access in connected applications. Preserve required records before changing mailbox access, transferring files, removing licences or deleting accounts. Recover devices or use an approved management action after checking ownership, retention and evidence needs. Record failures and any follow-up still required.
For Google Workspace, plan suspension, session controls and file handover using the relevant administrator tools. Check connected applications and retention requirements separately; do not delete the account before required data has been preserved.
$upn = "leaver@contoso.com"

Update-MgUser -UserId $upn -AccountEnabled:$false   # block new sign-ins
Revoke-MgUserSignInSession -UserId $upn             # revoke refresh tokens; verify app sessions separately
This is a partial example, not a complete offboarding script. An unattended implementation needs supported application permissions, a suitable service identity, error handling and verification of each result. Session revocation does not instantly end every application session.
/ 03
Google Workspace workflows can use the Admin SDK to create users and update supported directory settings. Group membership, organisational units, licences and shared-drive access need separate checks. A role change may require several updates, and the workflow must report failures or incomplete provisioning.
/ 04
Mostly what you already license. Power Automate and Logic Apps handle approval flows, PowerShell with Microsoft Graph handles identity and licence changes, and Azure Automation or Azure Functions run scripts on a schedule under a managed identity. Entra ID lifecycle workflows are an option where licensing covers them. For Google Workspace, Apps Script and the Admin SDK play the same roles.
/ 05
Use an authorised HR record or structured request to capture the person, role, effective date and approving owner. Validate those fields before the workflow runs. Missing or conflicting information should go to a person for review rather than triggering account changes automatically.
/ 06
With least-privilege service identities (managed identities rather than stored passwords), approval steps for anything beyond standard access, logs that go somewhere people actually look, alerts when a run fails, and a manual runbook for when the automation is down. A workflow that fails silently is worse than a paper checklist.
/ 07
We compare task frequency, effort, failure impact and the controls needed before automation. Priorities depend on the processes and risks identified during review.
Microsoft 365 entitlements can cover standard connectors, but premium connectors, unattended automation and the way a flow is owned or invoked can change the licence requirement. We check the connector set, execution model, users and capacity limits before confirming the design.
Then a structured form or a scheduled export becomes the trigger. It's less elegant, but it still removes most of the manual work and the re-typing errors.
Device provisioning can be included where the hardware, licences and management platform support it. For Windows Autopilot and Intune, registration, enrolment profiles, network access and application deployment need validation. Failed enrolment or missing applications require follow-up.
You can own them using the runbooks we hand over, or we maintain them under a support agreement. Either way, every workflow is documented: what triggers it, what it changes, who approves, and how to do it by hand.
Mostly scripting and workflow tools, because onboarding needs to be exact, not creative. AI helps at the edges, like reading a free-text request and filling in the right form, but the actions themselves run on rules.
/ Next step
Current process, volume, tools, connector availability, approval owner and common failure cases.